Time left until DPDPA obligations apply13 May 2027
209 days remaining

Privacy and consent you can prove.

Every consent, signed and verifiable.

Your named expertOne person who knows your set-up
Guided set-upWe configure it with you and train your team
One teamNo hand-offs when you need help
Always currentWe track the regulations for you
Independently assured

Certified for the way we handle your information.

ISO/IEC 27001Information security management

An internationally recognised standard for how an organisation protects information, from access control to incident handling.

SOC 2 Type IIControls tested over time

An independent auditor's report that our security controls were designed well and operated effectively across a review period.

Need the certificate or report for your vendor review? Ask us.

Start where you are

What are you working on?

Pick the closest fit. We will show where to look first.

Run the DPDPA day to day

  • Record consent for each purpose, with withdrawal
  • Answer data principal requests against due dates
  • Find and map where personal data lives
In action

See the solutions at work.

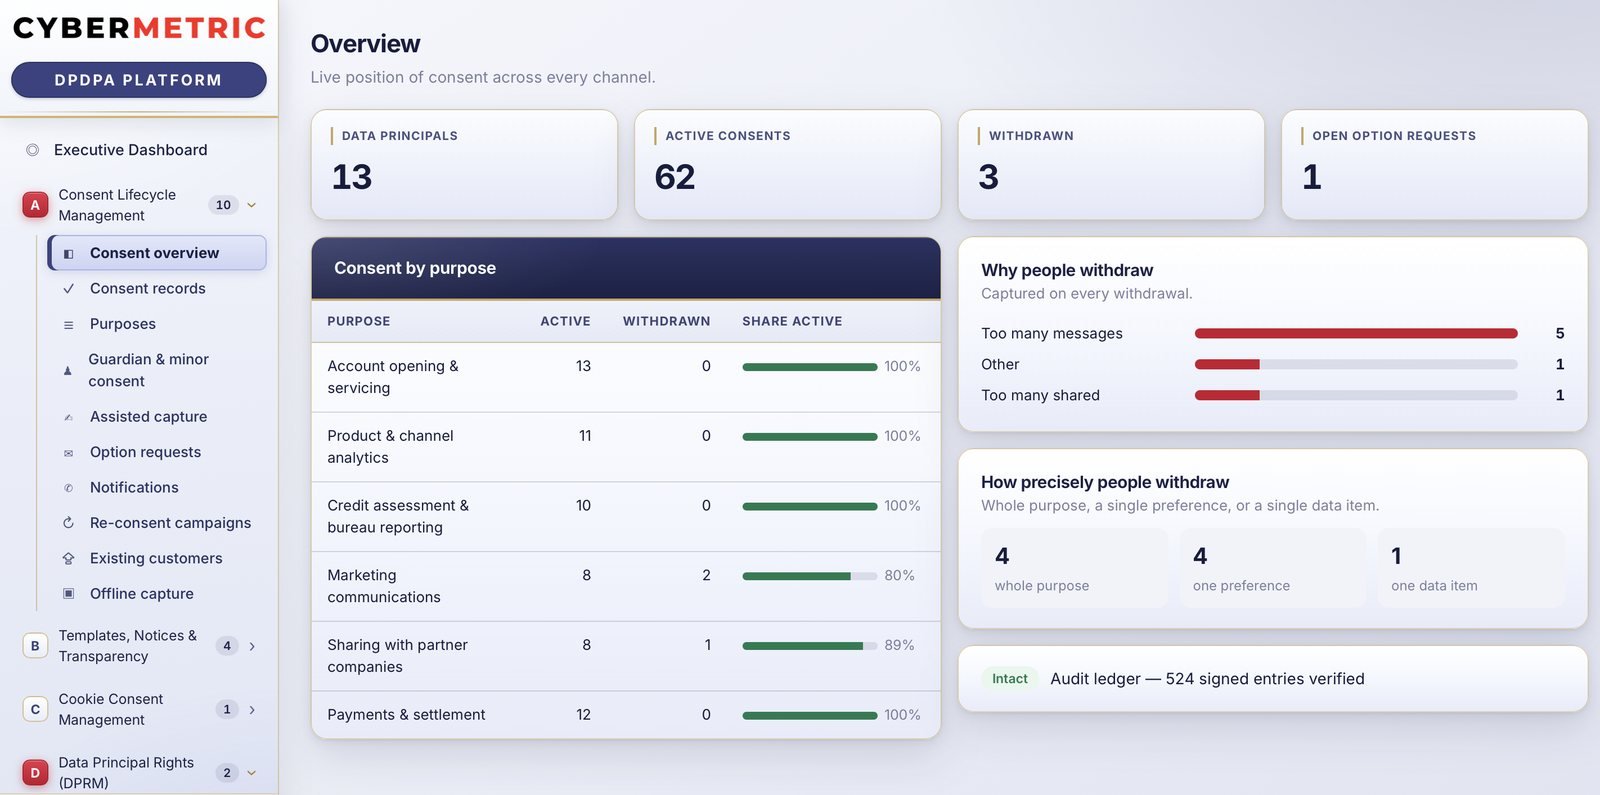
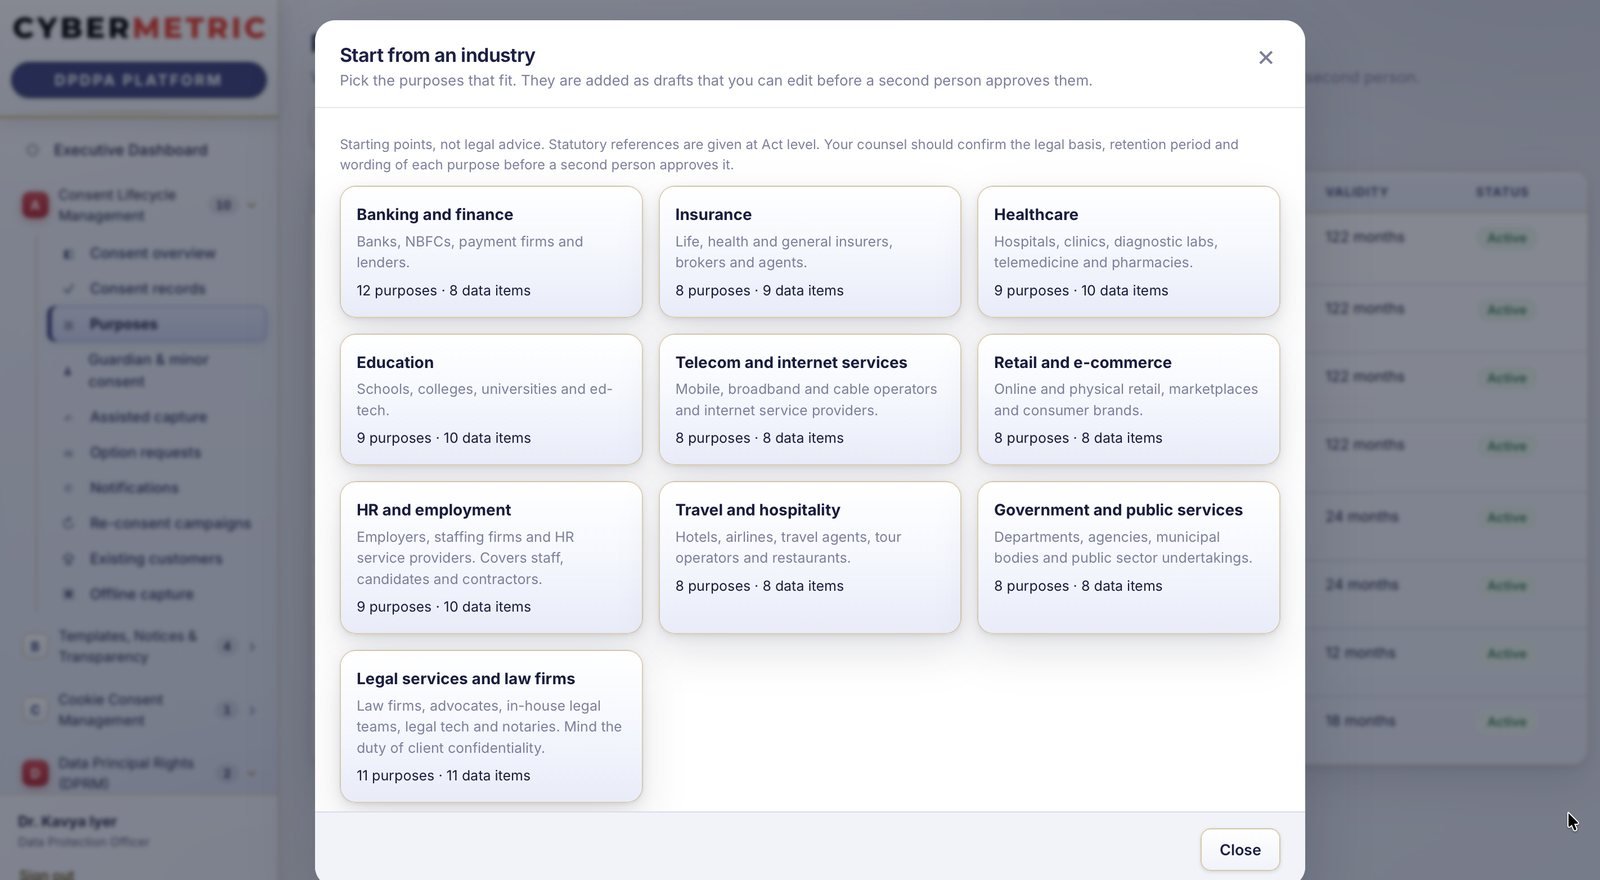
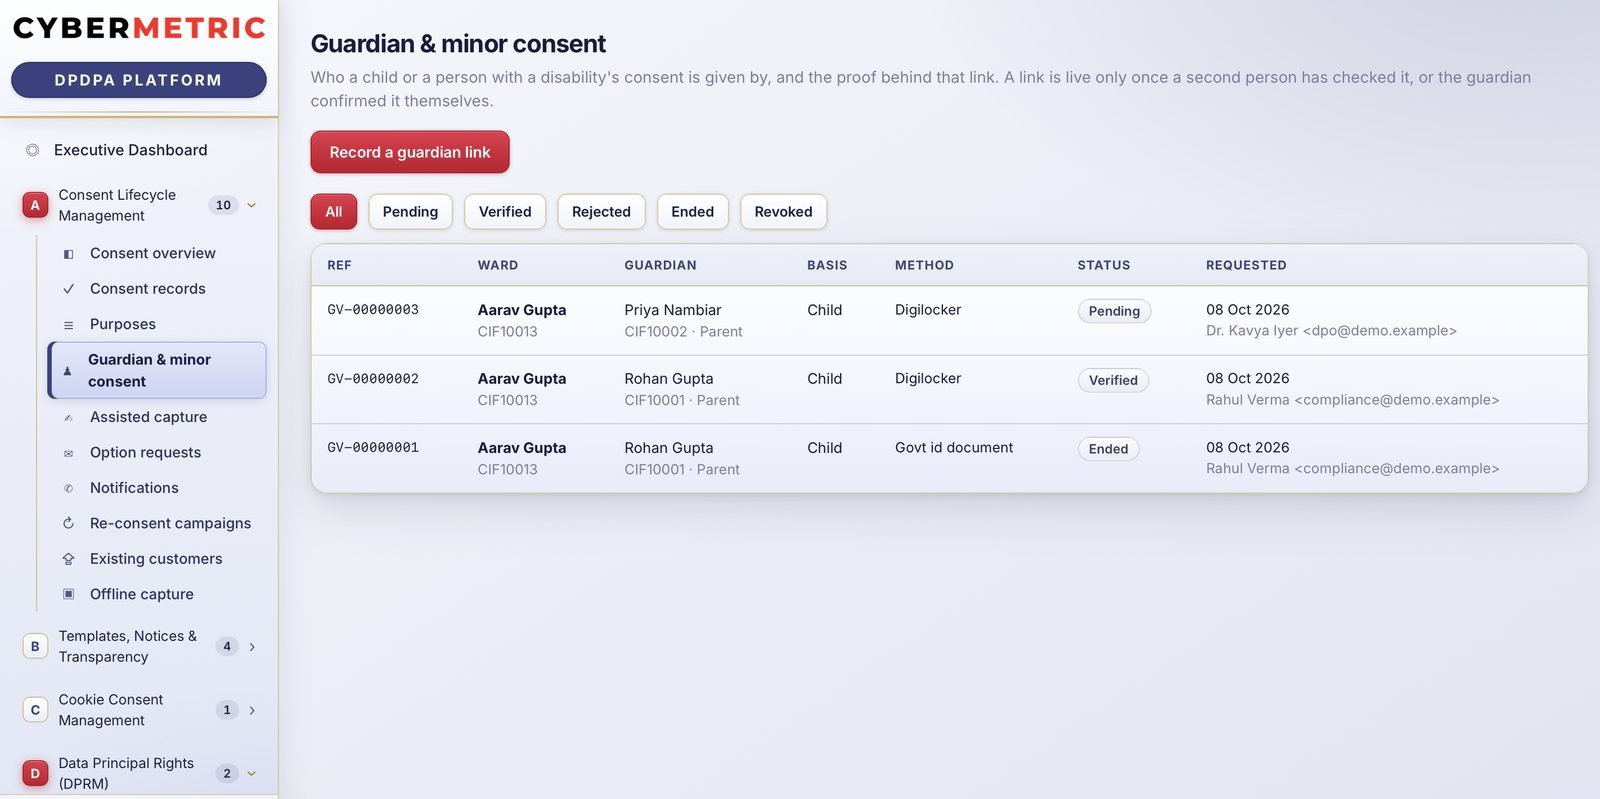
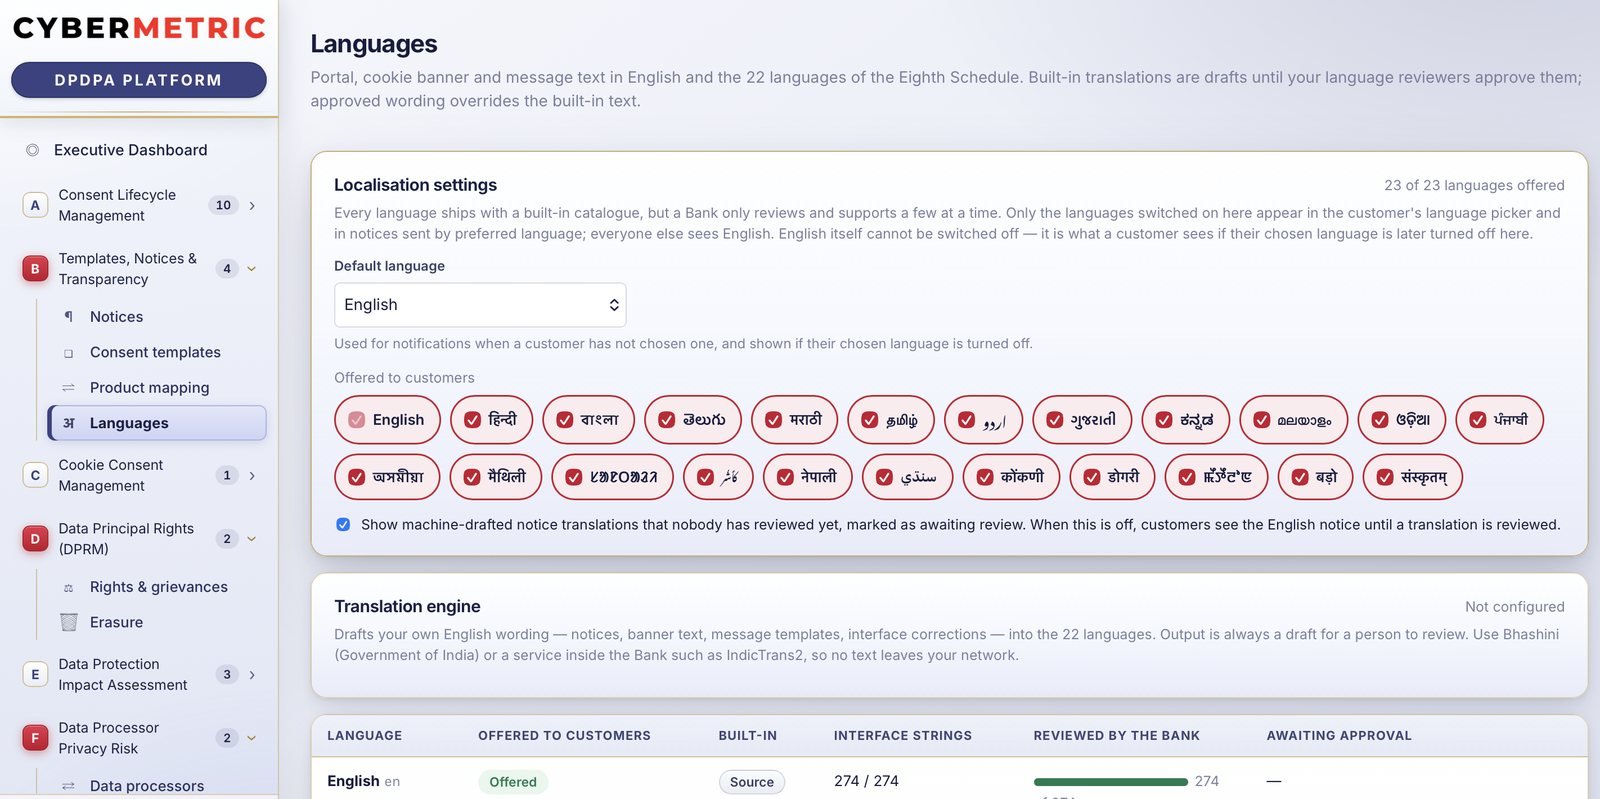
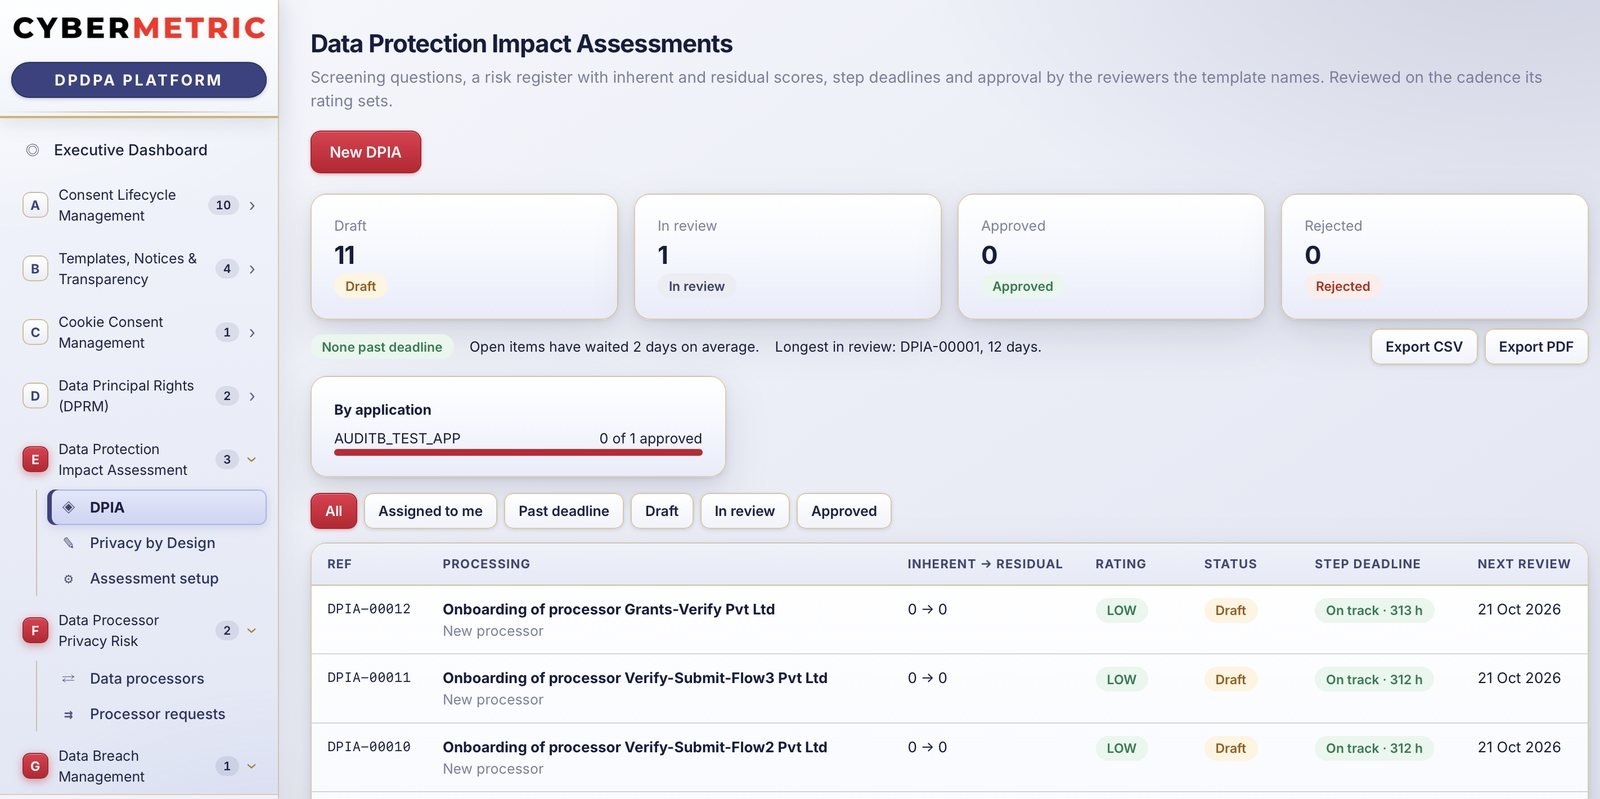
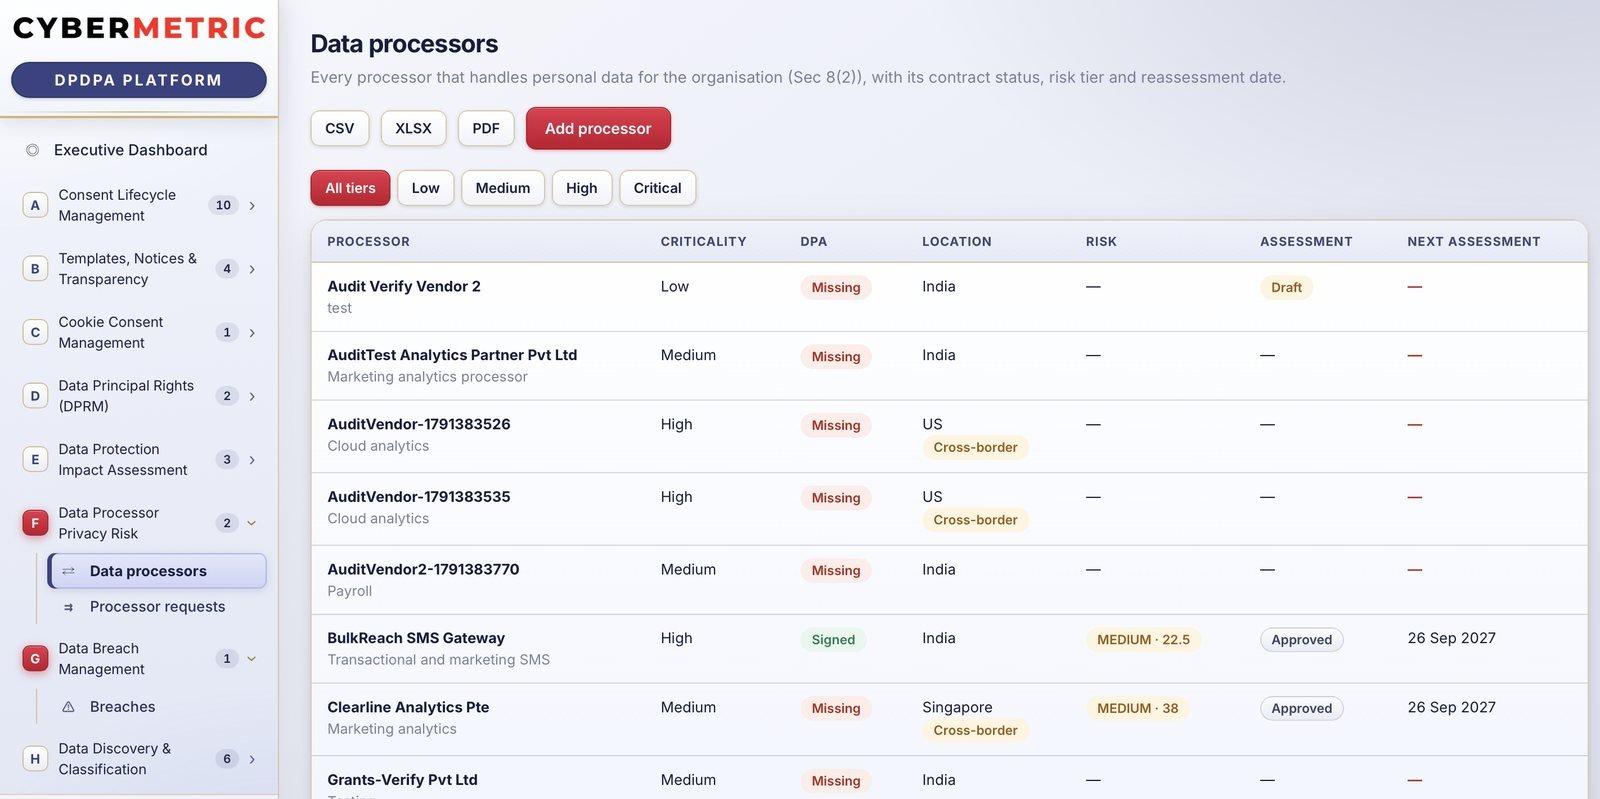
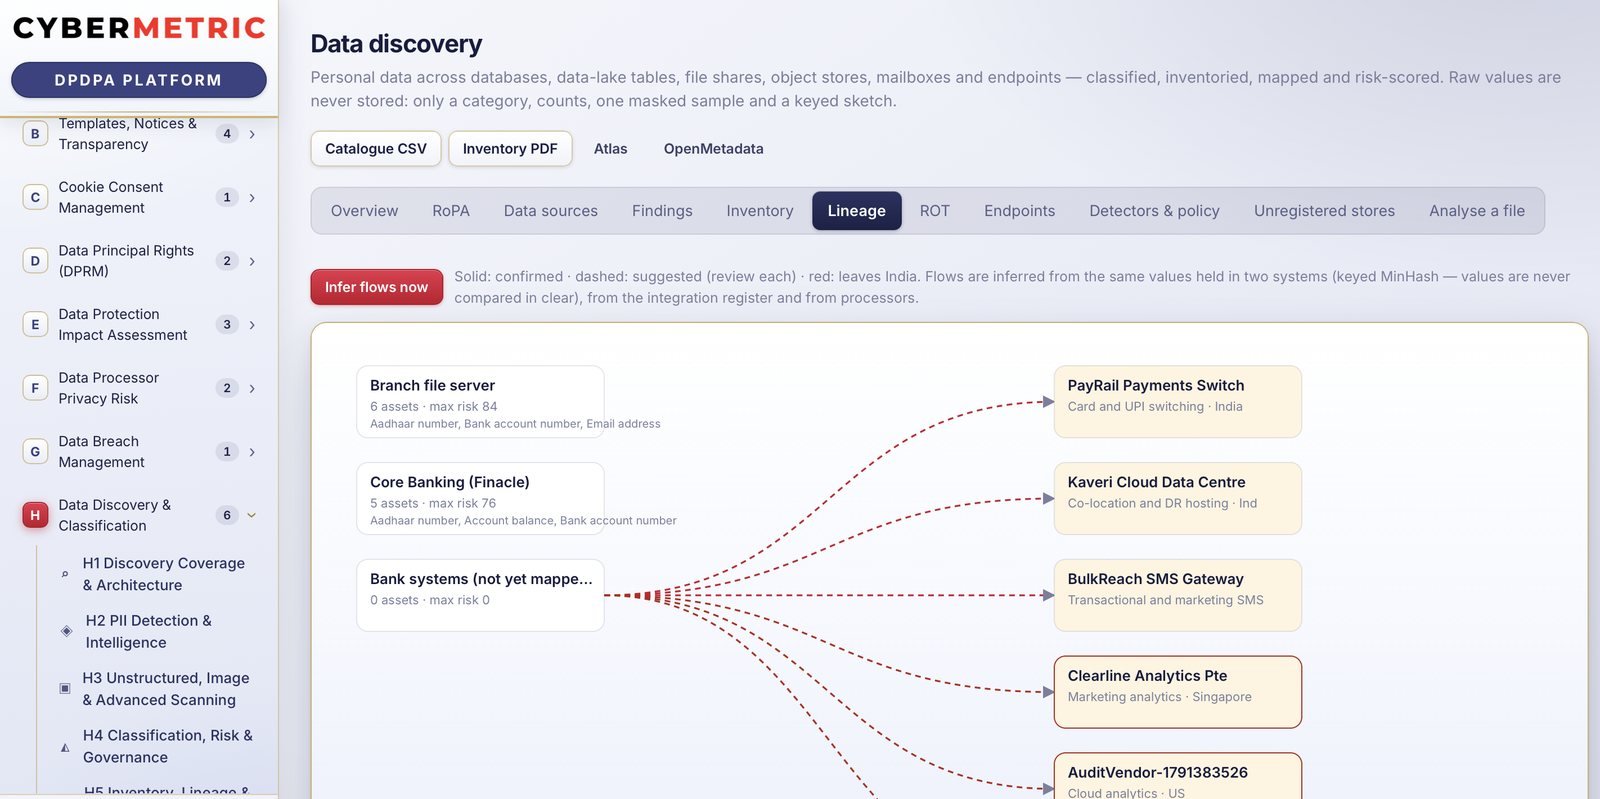
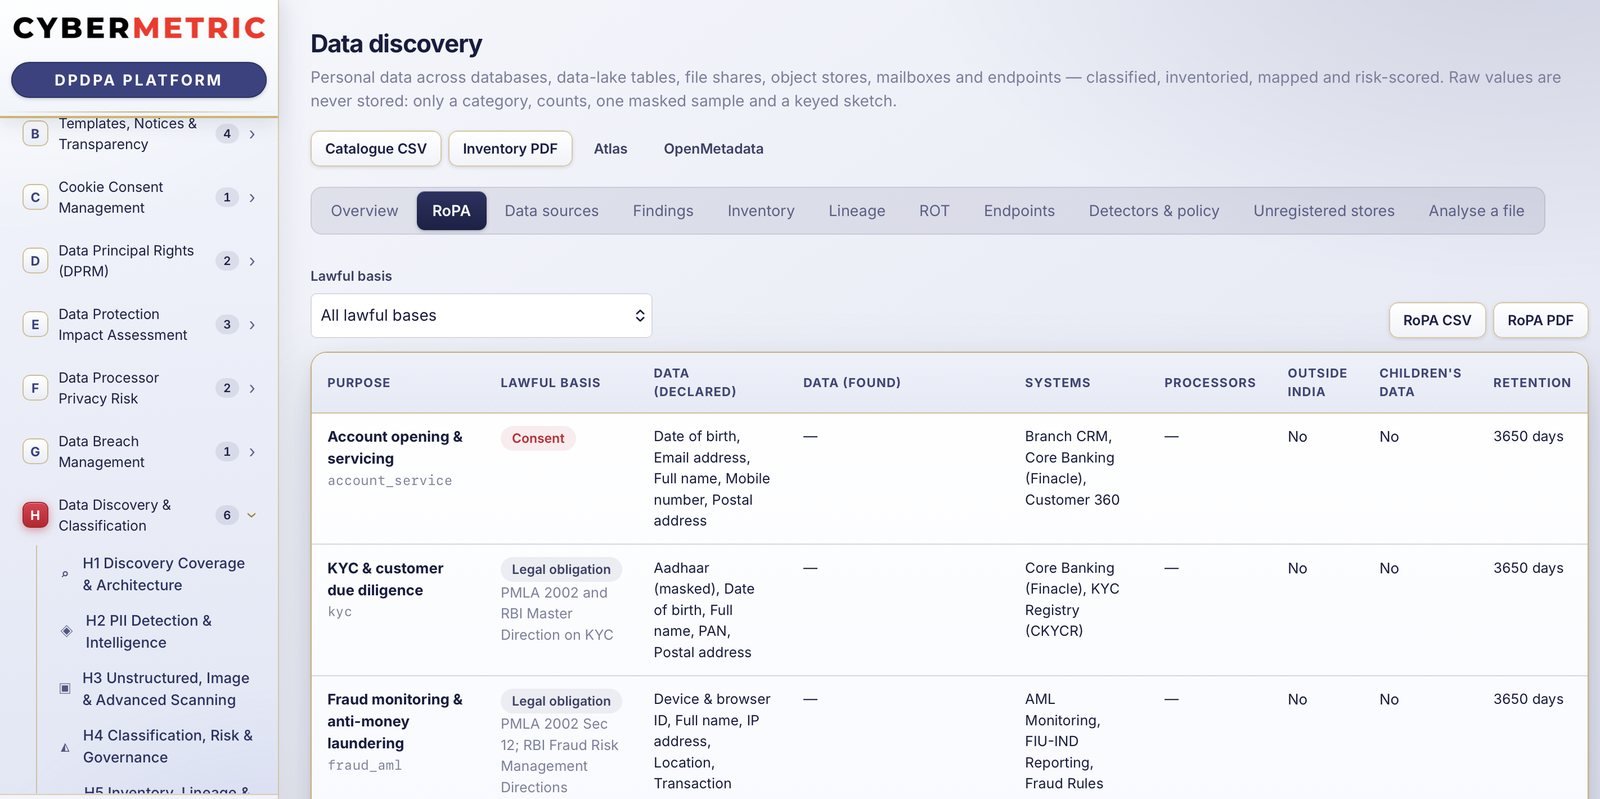
A look at the screens your teams would use every day. Drag to spin it, or use Pause.

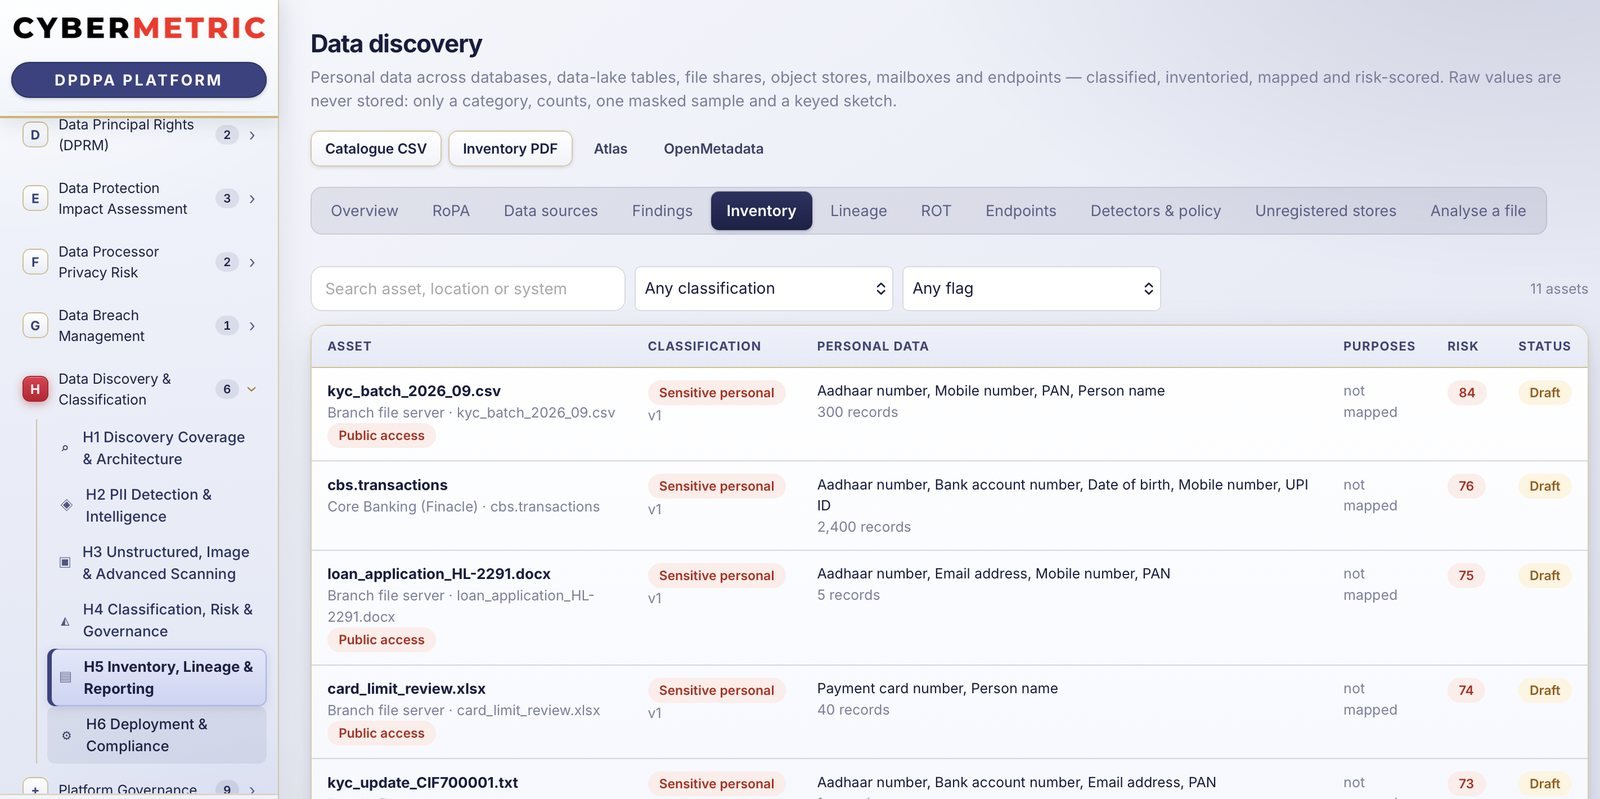
CyberMetric DPDPAExecutive dashboard

A single compliance score and grade, with the items that need attention listed by impact, each tied to its section of the Act.

Featured

Built for the regulations you actually face.

CyberMetric DPDPA

Consent, data discovery and rights management for the DPDPA.

CyberMetric DPDPA helps an organisation meet its obligations under India's DPDPA. It records consent, handles data principal requests, maps where personal data lives and keeps the evidence an auditor will ask for.

  • Consent lifecycle: purposes, records, guardian and minor consent, re-consent and offline capture
  • Notices and templates, in English and the 22 languages of the Eighth Schedule
  • Cookie consent management
  • Data principal rights, grievances and erasure, with due dates
CyberMetric DPDPA · Executive dashboard
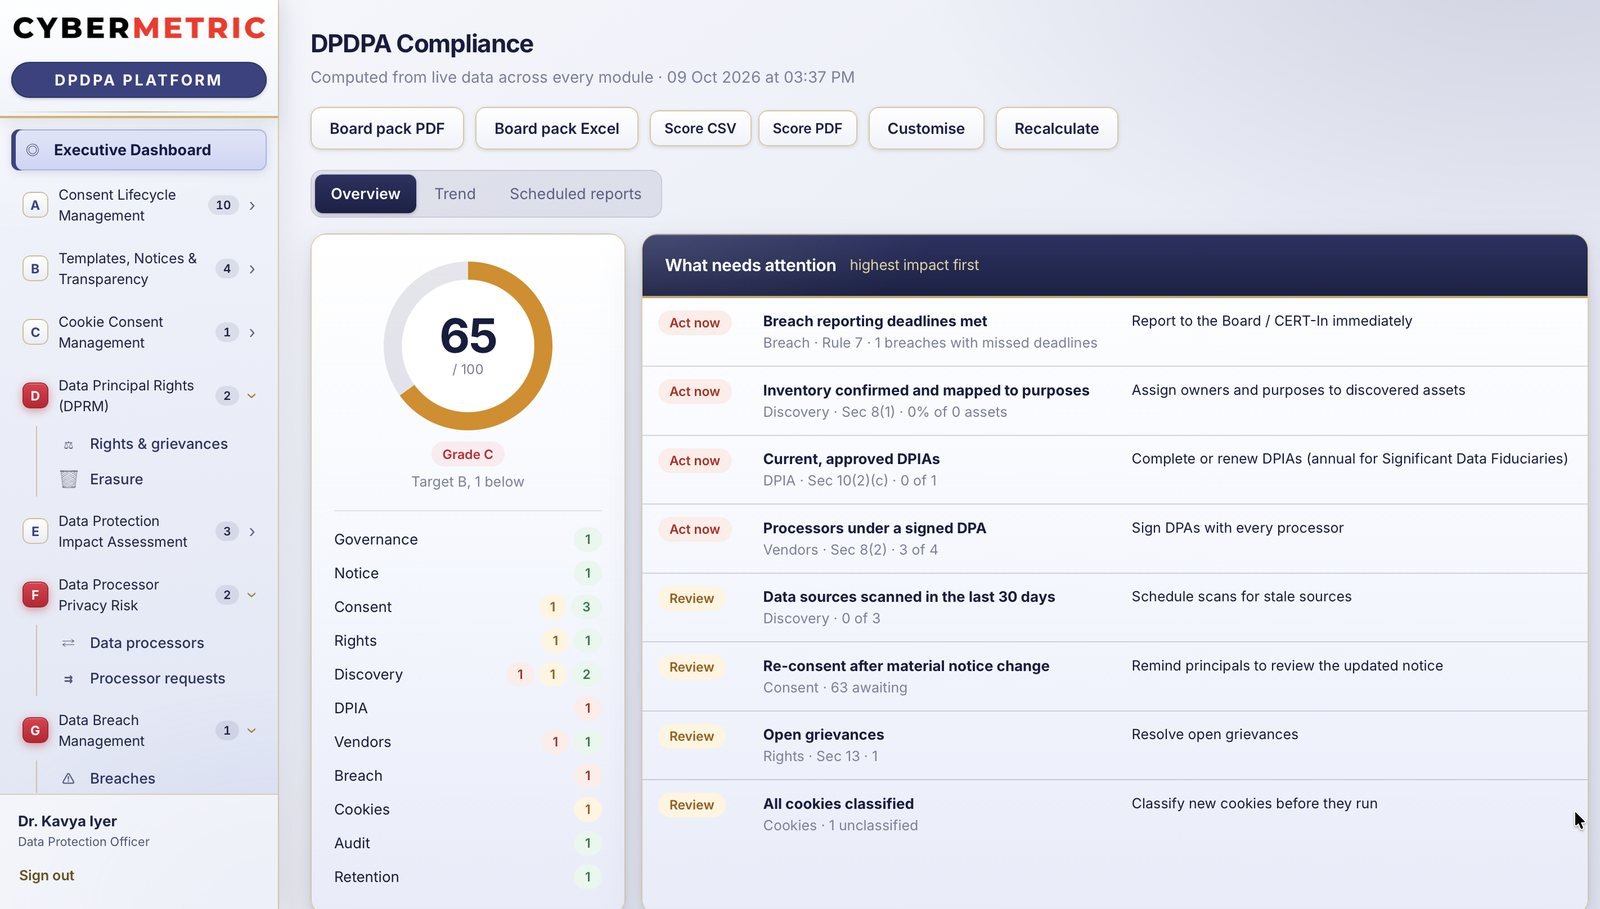
Executive dashboard in CyberMetric DPDPA

CyberMetric GRC

IRM and GRC automation with guided compliance project plans.

CyberMetric GRC automates governance, risk and compliance work in one easy-to-use application. It ships as SaaS or on-premise, with licence control held by the vendor.

  • SaaS and on-premise delivery
  • Project plans with milestones for each compliance framework, such as SOC 2 Type II
  • Progress that fills visibly as work completes
  • Standards watch that alerts the vendor admin to changes, with suggested updates
Support

You are never handed a login and left alone.

Choosing software for compliance is a decision about the people behind it as much as the solution. This is what working with us looks like.

Your own named expert

You always know who to call. The same person learns your systems, your teams and your deadlines.

Direct line to the builders

Questions and requests reach the product team, not a call centre. What you ask for shapes what we build next.

Training for every role

Data protection officers, auditors, legal advisers and administrators each get guidance for the work they do.

Reports your board can read

Plain-language summaries of where you stand, what is overdue and what to do next.

Updates when the rules change

We watch the regulations and ship the changes, so your team is not left reading amendments.

Privacy built in

When CyberMetric DPDPA scans your systems it keeps the category, a confidence score and one masked sample, never the raw value.

How it works

From first conversation to confident audit.

Four stages, with the same people alongside you at each one.

  1. Understand

    We learn how your organisation handles personal data and which regulations apply to you.

  2. Set up

    We configure the solution with you, connect your systems and load your policies.

  3. Go live

    We train the people who will use it every day and stay close through the first weeks.

  4. Stay supported

    We track rule changes, ship updates and review your progress with you on a regular basis.

SOC 2 readiness

SOC 2, run as a programme. Not a scramble.

Enterprise buyers ask for the report before they sign. CyberMetric GRC carries the plan, an owner for every control and audit-ready evidence, and a named expert stays beside you until an independent CPA firm issues the report.

  • 5Trust Services Criteria
  • CC1 to CC9mapped to controls
  • I and IIone plan underneath
  • SecurityCC1 to CC9
  • AvailabilityA1
  • Processing integrityPI1
  • ConfidentialityC1
  • PrivacyP1 to P8
Why CyberMetric

Built for India's law, not adapted to it.

How we differ from the two ways most teams cope today.

Spreadsheets and shared drivesGeneric global GRC suitesCyberMetric Labs
Built around India's DPDPANoOften adapted afterwardsYes, module by section
Proof of consent and withdrawalScattered recordsVaries by suiteConsent ledger with history
Rights requests with due datesManual trackingVaries by suiteOwners, due dates and an on-time rate
Finds where personal data livesSelf-reportedUsually separate toolingDiscovery feeding your data inventory
Tamper-evident audit trailNoVaries by suiteChained records, integrity shown on the dashboard
People beside you after go-liveYour own teamSupport deskA named expert and a direct line to the builders

A general comparison of approaches, not of any named vendor. Capabilities differ between suites, so check each one against your needs.

Platform

What every solution is built on.

Shared foundations so evidence, access and licensing behave the same way wherever you work.

Audit-ready evidence

Records keep their history, so a consent decision or a finding can be traced back to when and how it happened.

Role-based access

Roles such as administrator, auditor, compliance officer, data protection officer and legal adviser.

SaaS or on-premise

CyberMetric GRC runs in the cloud or inside your own environment, with licensing controlled by the vendor.

Guided by regulation

Modules map to the sections and controls they serve, so teams see which obligation a task answers.

AI where it saves time

AI assists with policy review and drafting. People stay in charge of every decision.

Easy to use

Clear navigation, visible progress and a short path from login to the work that is due.

Keep going

Where to next?

Pick a path. Each one takes a minute or two, and ends with a clear answer.

  1. ✓Explore
  2. 2Self-check
  3. 3Talk to us
Book a walkthrough

See it against your requirements.

Ask for a walkthrough, a pilot or a fit check for your regulator, your sector and your data.