CyberMetric DPDPA
Consent, data discovery and rights management for the DPDPA.
The clock is already running.
Readiness is a programme of months, not a weekend, and the penalties in the Act are set per breach.
Maximum penalties in the Schedule to the Digital Personal Data Protection Act, 2023.
What your team walks away with
A consent trail you can defend
Every consent decision, notice version and withdrawal is recorded with its history in a consent ledger.
Rights requests closed on time
Each request has an owner and a due date, and the on-time rate sits on your dashboard.
A map of where personal data lives
Connected databases and files are scanned, and the findings flow into your data inventory (RoPA).
Evidence on demand
A compliance score, a tamper-evident audit trail and plain-language reports your board can read.
Spreadsheets and inboxes, or one record you can show.
What changes when privacy work moves into a single system.
Beyond consent: control the data itself.
Consent and requests show you respect people's choices. Section 8(5) asks you to protect the data too. These four capabilities are how you show it.
Data classification
Label personal and sensitive data by category and sensitivity, so the right controls follow the data.
Data handling
Set how each class of data is used, shared, kept and erased, and keep handling consistent across teams and systems.
Data encryption
Protect personal data at rest and in transit, so an exposed file or copy is not readable.
Data lineage
Trace where personal data came from, where it moves and who has handled it, so requests and breach assessments start from facts.
Together they support the reasonable security safeguards the DPDPA requires under Section 8(5).
From scattered data to evidence you can show.
Connect
Link the databases, files and applications that hold personal data.
Discover
Rule-based scans find personal data and fill your data inventory.
Record
Capture notices and consent with versions, history and withdrawal.
Respond
Route rights requests to owners, against due dates.
Prove
A dashboard, a tamper-evident trail and reports your board can read.
The screens your team would use every day.
Swipe the screen sideways to see all of it.
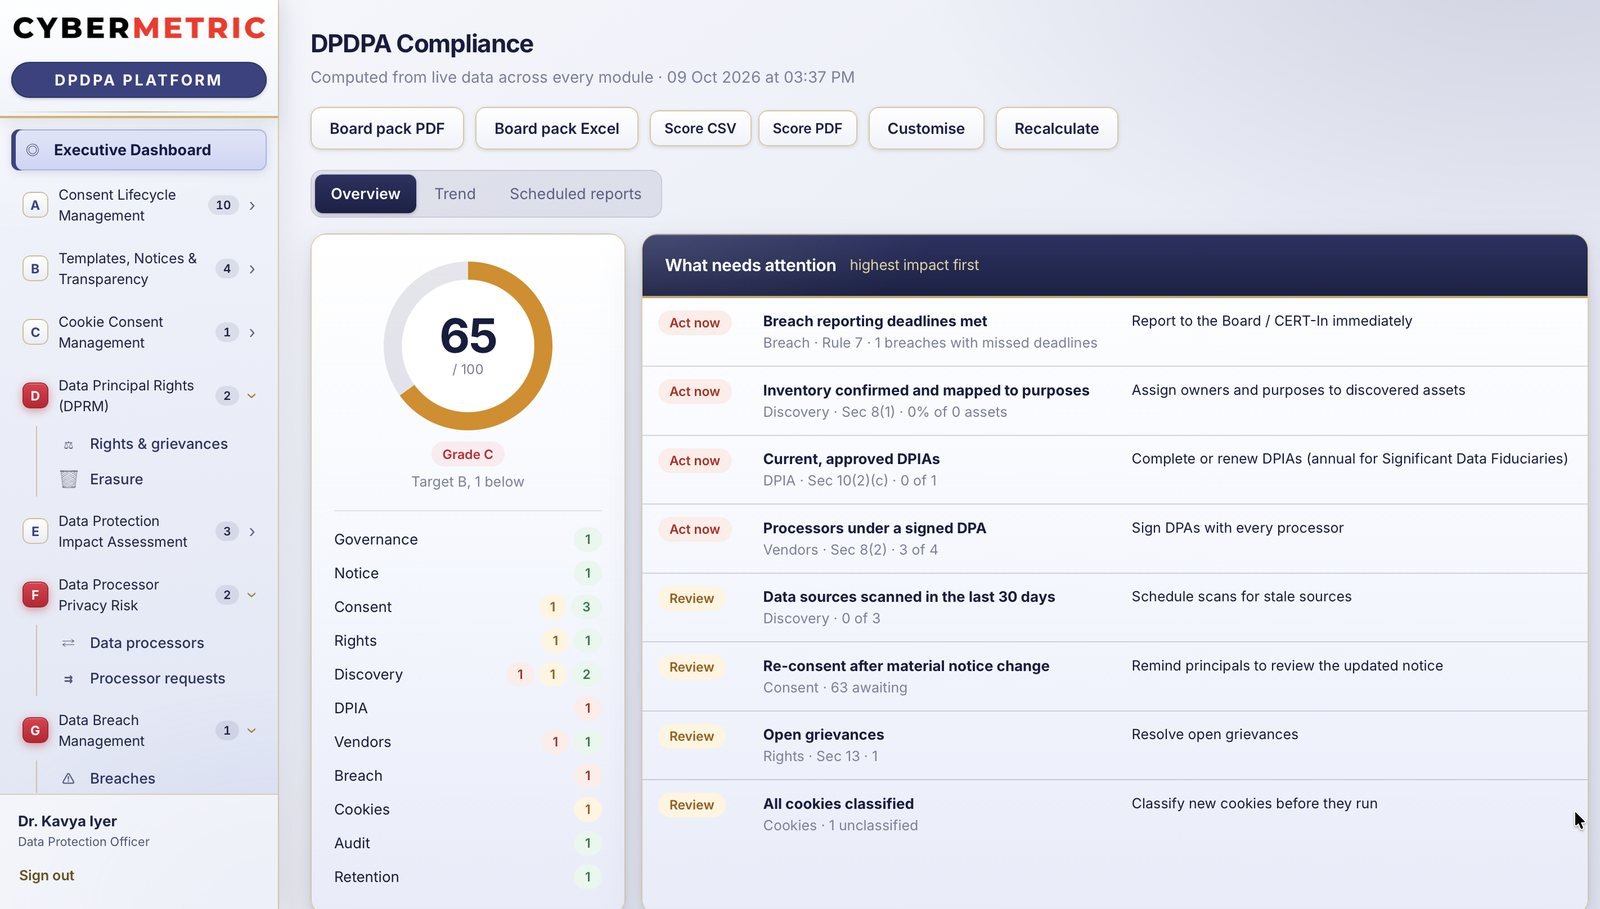
Executive dashboard. A single compliance score and grade, with the items that need attention listed by impact, each tied to its section of the Act.
How ready are you today?
Nine questions from our C-suite self-assessment toolkit, about a minute. Your answers stay on this page and are not sent anywhere unless you choose to book.
Have you appointed a Data Protection Officer or designated individual responsible for DPDPA compliance?
Want to see this on your own systems?
Book a walkthroughWhere the Act meets the solution
Each module is built around the section it serves, so your team can see which obligation a task answers.
Eight modules, one licence.
Each module is a lettered area of the platform, so your team always knows where a task lives.
Consent Lifecycle Management
Capture, record and honour consent for every purpose, from first notice to withdrawal and renewal.
Templates, Notices & Transparency
Clear notices and templates your principals can read, in English and the 22 languages of the Eighth Schedule, reviewed before use.
Ask about this moduleCookie Consent Management
A cookie banner and cookie consent, with new cookies classified before they run.
Ask about this moduleData Principal Rights (DPRM)
Lodge, assign and close rights requests and grievances against their due dates, and carry out erasure.
Data Protection Impact Assessment
DPIAs with inherent and residual scores, step deadlines, approval and the next review date.
Data Processor Privacy Risk
Every processor with its contract status, risk tier, location and reassessment date.
Data Breach Management
Record breaches and track reporting deadlines, with missed deadlines raised on the dashboard.
Data Discovery & Classification
Find personal data, classify it, trace its lineage and keep the inventory and record of processing current.
From first call to live, with the same people.
Intro call
We listen: your sector, your systems and your deadline.
Tailored walkthrough
A guided tour built around your use case, with your questions answered live.
Pilot or fit check
Test it on a sample source or a framework plan and see real results before you commit.
Rollout with your expert
A named expert configures it with you, trains your people and stays beside you after go-live.
Built to be trusted
Detection you can explain
Rule-based matching, not a black box. The solution publishes how it detects personal data and which categories it cannot.
Raw data is never stored
Discovery keeps the category, a confidence score and one masked sample, never the raw value.
A tamper-evident audit trail
Records are chained together so any change can be detected, and the dashboard shows whether the trail is intact.
A role for every function
Seven roles, including administrator, auditor, compliance officer, data protection officer and legal adviser.
Built for the people who answer for it.
Banks, hospitals and enterprises preparing for the Digital Personal Data Protection Act.
Data Protection Officer
One view of consent, rights requests and readiness.
Legal and policy
Notices, policies and processor agreements with version history.
CISO and IT
Where sensitive data sits, and a trail of who changed what.
Audit and compliance
Evidence on demand, without chasing teams.
Where to next?
Pick a path. Each one takes a minute or two, and ends with a clear answer.
- ✓Explore
- 2Self-check
- 3Talk to us
See CyberMetric DPDPA against your requirements.
Tell us a little and we will arrange a conversation with the people who build and support it.
What we will cover
- Your sector, systems and timeline
- A walkthrough built around your use case
- Where you stand against the DPDPA's obligations
- A clear next step, with no obligation
Helpful to bring
- A rough list of systems that hold personal data
- Who owns privacy in your organisation today
- Your target date for readiness
Need the certificate or report for your vendor review? Ask us.